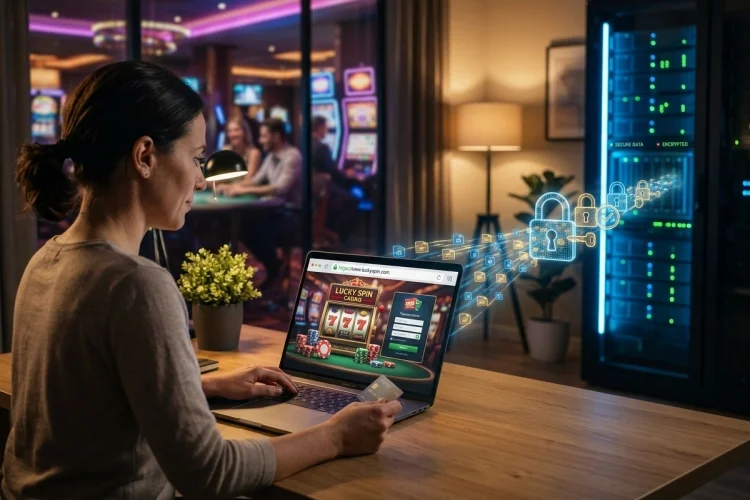
You click “Deposit,” enter personal details, and press submit. Within seconds, information moves from your device through the internet to several systems. Most of that technical process remains completely invisible.
Learning What Is SSL Encryption explains one of the technologies designed to protect that journey. Despite the familiar name, modern secure websites generally rely on TLS rather than the outdated SSL protocol.
TLS creates encrypted HTTPS connections that help protect confidentiality, verify domains, and preserve data integrity. For casino players, understanding what this technology can – and cannot – do is especially useful.
SSL and TLS Are Not Exactly the Same Thing
“SSL encryption” remains one of the most commonly used phrases in website security.
Technically, it is outdated terminology.
SSL was the earlier protocol family. TLS replaced it and continues to provide modern transport security.
The UK Information Commissioner’s Office says organisations should not use any SSL version for public-facing HTTPS services because all SSL versions contain known vulnerabilities.
Its current guidance recommends TLS and identifies TLS 1.3 as the preferred modern option where appropriate.
So when a casino advertises “SSL encryption,” the better technical question is whether its website uses properly configured modern TLS.
The terms remain mixed in everyday marketing, but the distinction matters for securty.
The Secure Connection Begins Before You Log In
TLS begins working before you type a password.
When your browser connects to an HTTPS website, it and the server first establish how they will communicate securely.
Part of the process involves checking the server’s digital certificate.
The browser then participates in establishing cryptographic keys that can protect the session.
NIST describes TLS as providing confidentiality, authentication, and integrity between connected clients and servers.
This means the connection is designed to answer three fundamental questions:
Can outsiders easily read the data?
Can the browser authenticate the server?
Can undetected manipulation of the communication be prevented?
TLS addresses these problems together rather than acting only as a password scrambler.
Certificates Help Authenticate the Domain
Imagine typing what appears to be your casino’s address.
Your browser needs a way to determine whether the server can present valid credentials for that domain.
TLS certificates provide part of this process.
Mozilla explains that websites using HTTPS rely on TLS server certificates to demonstrate control over a domain and enable protected encrypted communication.
Browsers use a chain of trust involving recognised certificate authorities.
A certificate authority verifies the required domain control before issuing certificates.
Let’s Encrypt’s ACME system, for example, requires an applicant to prove control over the relevant domain before a certificate can be issued.
That helps prevent an arbitrary server from simply claiming any domain name it wants during an HTTPS connection.
Encryption Makes Intercepted Traffic Harder to Read
Think about connecting to a casino over a network.
Your browser might send account information, session data, or other sensitive content toward the casino.
TLS encrypts that communication.
If someone intercepts the network traffic without the necessary cryptographic information, they should not receive a convenient, readable copy of everything transmitted.
The ICO describes this as encryption in transit and specifically recommends encrypted communication protocols such as HTTPS when personal information moves across networks.
This matters particularly when people use shared or otherwise untrusted network environments.
However, encryption does not make unsafe networks magically risk-free.
Other attacks, compromised devices, phishing pages, and stolen credentials can bypass the protecton provided by encrypted transport.
Encryption Protects Data in Transit, Not Everywhere
This distinction is critical.
TLS primarily protects information while it moves between endpoints.
After data reaches the casino server, the server needs to process it in a usable form.
At that stage, other controls become important.
The casino may need database encryption, strict employee permissions, authentication controls, monitoring, backups, network protections, and incident-response systems.
The ICO explicitly notes that HTTPS without additional protection does not mean information remains encrypted during storage.
So when a website says it “uses SSL encryption,” that statement tells you only part of its cybersecurity story.
A player database can still be poorly protected even if the login page has perfect TLS.
Strong casino security must cover data at rest as well as data moving across the internet.
How TLS Relates to Casino Payments
Payment transactions make secure communication especially important.
Players may submit financial information through casino websites or payment interfaces.
TLS helps protect applicable information while it travels between the browser and online service.
However, card-data security involves additional industry requirements beyond HTTPS.
For example, payment environments can fall under PCI DSS requirements covering the protection of payment account data.
Likewise, the UK Gambling Commission identifies systems that handle credit or debit card details, authentication information, and player balances as critical gambling systems requiring appropriate security controls.
That is why “encrypted checkout” should not be interpreted as the casino’s entire financial-security system.
Transport encryption is one layer within a larger payment and account infrastructure.
TLS Also Helps Prevent Undetected Tampering
Confidentiality is only half the story.
Suppose information leaves your browser but is changed before reaching the casino server.
That creates a different security problem.
TLS includes integrity protections designed to help detect unauthorised modifications during communication.
NIST specifically identifies integrity as one of TLS’s major security properties alongside confidentiality and authentication.
This protects more than passwords.
Account requests, session communications, and other transmitted information benefit from a channel that resists unnoticed manipulation.
A modern HTTPS connection therefore provides a combination of encrypted content and mechanisms for validating the communication.
That broader function is why TLS is foundational to modern web security.
What the Browser Security Indicator Really Means
Modern browsers provide visual information about connection security.
Exactly how that information appears can vary between browser versions.
The important distinction is between a secure connection and a trustworthy business.
Mozilla explains that HTTPS certificates verify domain control and enable encrypted TLS communication.
They do not conduct a complete investigation into whether the website provides fair casino games, pays withdrawals correctly, or holds the gambling licence it claims.
A scam operator can own a domain.
If it controls that domain, it can potentially obtain a valid certificate for it.
Therefore, a browser showing a secure connection should be interpreted as:
“This connection to this domain is protected.”
It should not be interpreted as:
“This casino has been independently proven trustworthy.”
That second question requires seperate verification.
Why Certificate Warnings Should Not Be Ignored
Sometimes a browser displays a full security warning rather than loading a page normally.
Several issues can cause this.
A certificate could be expired, issued incorrectly, configured for another domain, or otherwise fail validation.
In such a situation, bypassing the warning and entering sensitive information is risky.
Certificates have validity periods and must be managed correctly.
Let’s Encrypt, for example, describes certificate issuance, renewal, and revocation as ongoing parts of its certificate lifecycle.
A legitimate casino experiencing a certificate problem may simply have made a technical mistake.
But from the player’s perspective, there is little reason to submit financial or identity information until the issue is resolved.
Let the operator fix the connection first.
Modern Casino Security Goes Beyond TLS
Remote gambling infrastructure contains much more than a public website.
Back-end systems may process account balances, authentication data, payment information, game transactions, and personal details.
Regulators can therefore require broader controls.
The UK Gambling Commission’s remote technical standards currently base relevant security requirements on Annex A of ISO/IEC 27001:2022. These requirements cover critical systems that store, process, transmit, share, or retrieve sensitive customer information.
Applicable remote licence holders are also subject to annual third-party security audits against particular requirements.
This highlights why focusing entirely on SSL can create a false sense of completeness.
TLS secures an important communication channel.
Professional cybersecurity must protect the systems at both ends too.
Can Players Verify TLS Themselves?
You can perform several basic checks without understanding cryptography.
First, confirm that the address uses HTTPS and that your browser does not report a certificate problem.
Then verify that the domain is exactly the one you intended to visit.
Look carefully for misspellings.
Keep your browser updated because older browsers may lack support for newer protocols or security improvements.
You can also inspect certificate information through browser controls if you want more detail.
But technical verification should not stop there.
Confirm the casino’s licence separately through the relevant regulator and avoid following unexpected login links from emails or messages.
A perfectly encrypted phishing site can still steal the password you voluntarily enter.
TLS cannot protect against every human mistake.
Why “256-Bit SSL” Marketing Can Be Misleading
Casino websites sometimes advertise phrases such as “256-bit SSL security.”
These statements may sound impressive, but one number does not describe an entire security configuration.
Modern TLS security depends on protocol versions, cipher suites, certificate configuration, key management, implementation quality, and other factors.
NIST’s TLS guidance discusses protocol configuration and recommended cryptographic algorithms rather than reducing secure TLS deployment to one marketing number.
A technically sound TLS implementation is more important than a large number printed beside a padlock graphic.
Players do not need to audit cryptography themselves.
What matters is avoiding outdated technology and choosing regulated operators with broader, independently assessed security controls.
SSL Does Not Protect You From Every Threat
TLS is powerful, but its job has boundaries.
It cannot stop you from entering your password into a convincing phishing site with its own valid certificate.
It cannot prevent malware already installed on your computer from reading information at the endpoint.
It cannot guarantee that a casino’s internal employees have appropriate permissions.
And it cannot prove that games are fair.
These problems require other protections such as anti-phishing awareness, endpoint security, access controls, secure software development, regulatory oversight, and game testing.
This is why cybersecurity is often described as layered defence.
No single technology should be expected to solve everything.
The visable HTTPS connection is simply one layer players can check themselves.
What Is SSL Encryption is easier to answer once the terminology is updated: modern websites use TLS to secure HTTPS connections, while old SSL protocols should no longer be used.
TLS helps provide confidentiality, integrity, and server authentication for information travelling online.
When assessing a casino, check HTTPS but go further – verify the domain, licence, privacy practices, and account-security features before sharing sensitive data.